Home · Technology · Oct 30 archive
Security Flaw 'SMS of Death' Can Crash Android Phones
· Confirmed
In Short: Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls.
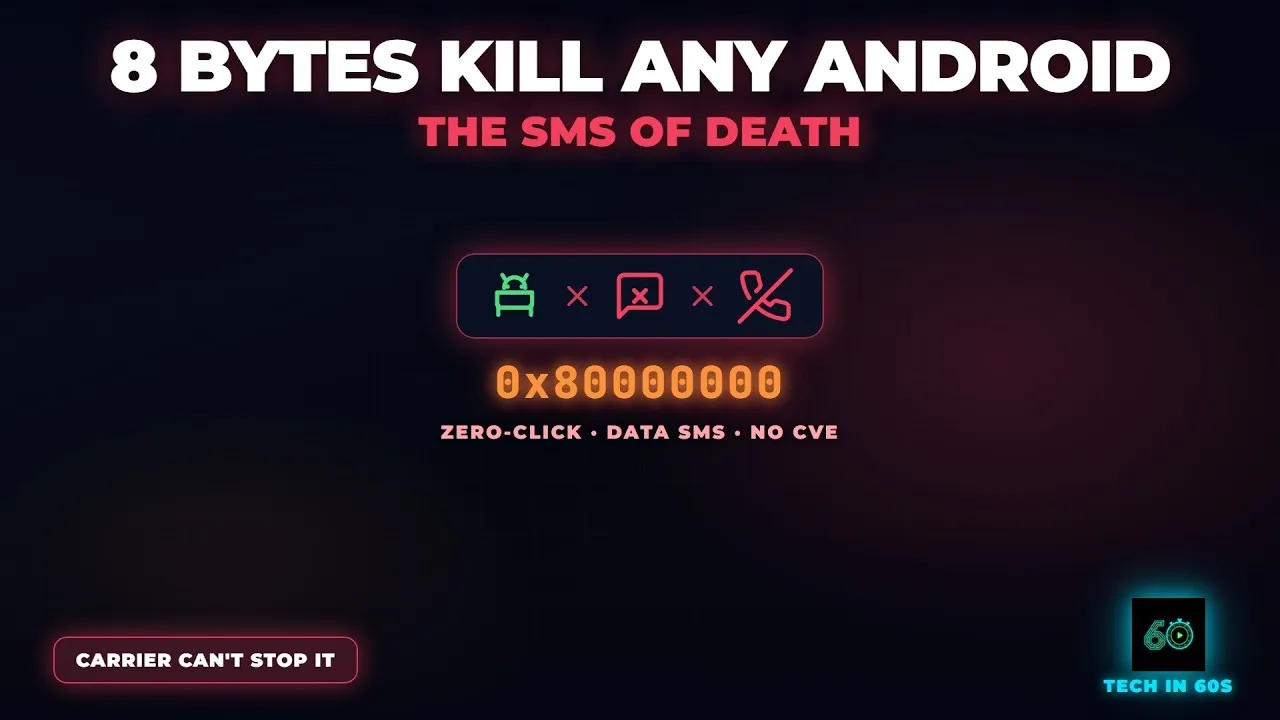
Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls. The vulnerability, known as 'SMS of Death,' can leave a phone practically unusable after receiving around 20 such messages.
According to Blaszczyk, the flaw involves a specially crafted text message that Android struggles to process, leading to repeated crashes of the com.android.phone process, which manages calling and mobile network activities. This can cause dropped calls and temporary loss of mobile network services, including emergency calls.
The bug, which sits in WapPushOverSms, the part of Android’s telephony framework that processes WAP Push messages, requires no user interaction and works remotely. A single malformed message can crash the com.android.phone process, causing it to crash on every boot.
Researchers tested the vulnerability on Google Pixel 9 and various Samsung Galaxy devices. The malicious message does not appear in the user’s SMS inbox, making it undetectable. Once the phone receives the message, it repeatedly tries to process it, leading to a reboot loop.
Google developed a fix for the issue on June 15 and included it in October’s Android security updates for versions 14 through 17. However, until the update reaches users, a single malformed message can cause the phone to crash repeatedly, requiring a factory reset or an involved recovery procedure.
The privacy-focused Android distribution GrapheneOS shipped the fix in its own security preview releases in mid-July and stated that the patch is part of the upcoming November 2026 Android Security Bulletin. Google, however, marked the report 'Won’t Fix' and treats it as a non-security issue, according to the researcher’s disclosure site.
The 'SMS of Death' exploit code is now public, and attackers can leverage SMSes to target victims using a proof-of-concept app made available on GitHub. This app remotely and silently sends a crafted 8-byte WAP Push PDU over SMS to a target handset.
The impact of this vulnerability is significant, as it can leave users unable to make calls or access emergency services until the phone is reset or repaired.
What this adds
The vulnerability, known as 'SMS of Death,' can leave a phone practically unusable after receiving around 20 such messages, according to Blaszczyk.
Background
Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls.
What's confirmed
- Security researcher Mark Blaszczyk discovered the flaw, which involves a specially crafted text message that Android struggles to process.
- Because Android can keep trying to process the same malicious message, the crash can happen repeatedly.
- Dubbed SMS of Death, the zero-click denial-of-service bug sits in WapPushOverSms, the part of Android’s telephony framework that processes WAP Push messages.
- The privacy-focused Android distribution said it shipped the fix in its own security preview releases that month, and that the patch is part of the upcoming November 2026 Android Security Bulletin.
- That throws an uncaught NegativeArraySizeException and kills the com.android.phone process.
- “A single malformed WAP Push SMS crashes com.android.phone on Android, dropping active calls (including emergency calls), with zero interaction from the victim,” Mark Blaszczyk, a security researcher (@sourone), said in a report.
- The bug requires no user interaction, the exploit works remotely, and often bricks the device – recovery requires connecting to the phone using Android Debug Bridge (ADB), according to the researcher.
What's still developing
- Imagine dialing 911, only for your phone to suddenly drop the call.
- That’s the frightening scenario behind SMS of Death, a newly disclosed Android vulnerability that lets attackers remotely disrupt phones without the victim lifting a finger.
- Affiliate links on Android Authority may earn us a commission.
- Try searching for other cybersecurity topics or keywords.
- Android then tries to create a byte array of that size.
- The author disclosed the bug responsibly in May, 2026.
- A pair of Gemini app updates today brings the latest design to all Android devices, while file generation sees a big upgrade.
- Meanwhile, the Gemini app now lets you “generate, preview, and edit files right within” chats.
- File creation and editing are live for “users in all languages where the Gemini app is available.” FTC: We use income earning auto affiliate links.
- This updated design was first introduced on phones with Gemini Intelligence (Pixel 11) and is now available on all other devices we checked today.