Home · Technology · Oct 30 archive
Security Flaw Discovered: SMS Can Crash Android Phones
· Confirmed
In Short: Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls.
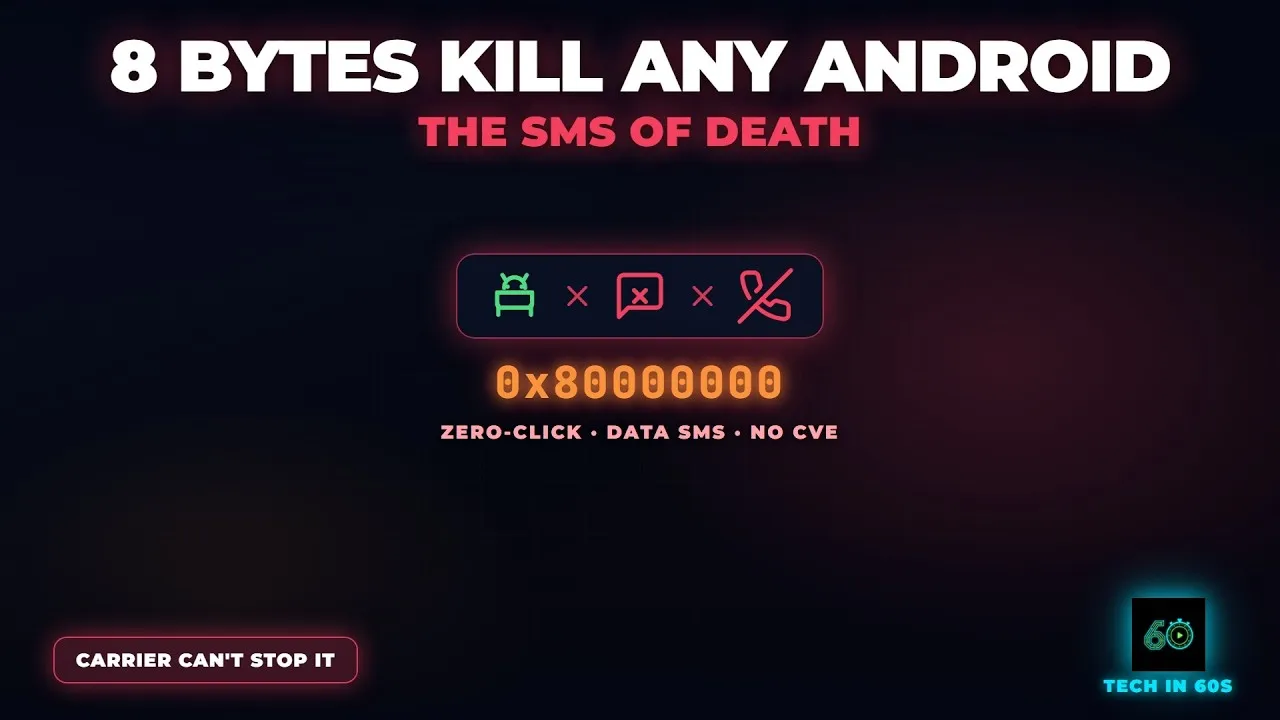
Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls.
According to Blaszczyk, the vulnerability, known as 'SMS of Death,' can leave a phone practically unusable after receiving around 20 such messages.
The flaw lies in WapPushOverSms, a part of Android’s telephony framework that processes WAP Push messages. When a malformed message is received, it triggers an uncaught NegativeArraySizeException, which kills the com.android.phone process.
This process handles calling and cellular service, so a crash can drop any call in progress, including emergency calls.
Blaszczyk explains that because Android keeps trying to process the same malicious message, the crash can happen repeatedly, potentially trapping the phone in a bootloop.
Google developed a fix for the issue on June 15, and included it in October’s Android security updates for versions 14 through 17.
GrapheneOS, a privacy-focused Android distribution, shipped the fix in its own security preview releases and stated that the patch will be part of the upcoming November 2026 Android Security Bulletin.
However, until the update reaches users, a single malformed message can kill the com.android.phone process, causing it to crash on every boot.
The researcher also released a proof-of-concept 'SMS of Death' app on GitHub, which remotely and silently sends a crafted 8-byte WAP Push PDU over SMS to a target handset.
The exploit code is now public, and recovery from the bug often requires connecting to the phone using Android Debug Bridge (ADB) or a factory reset.
Mark Blaszczyk warns, “A single malformed WAP Push SMS crashes com.android.phone on Android, dropping active calls (including emergency calls), with zero interaction from the victim.”
What this adds
The vulnerability highlights the potential risks of zero-click attacks on mobile devices, where attackers can exploit flaws without user interaction.
What's confirmed
- Security researcher Mark Blaszczyk discovered a critical flaw in Android that can crash phones with a specially crafted text message, potentially disrupting emergency calls.
- According to Blaszczyk, the vulnerability, known as 'SMS of Death,' can leave a phone practically unusable after receiving around 20 such messages.
- The flaw lies in WapPushOverSms, a part of Android’s telephony framework that processes WAP Push messages. When a malformed message is received, it triggers an uncaught NegativeArraySizeException, which kills the com.android.phone process.
- This process handles calling and cellular service, so a crash can drop any call in progress, including emergency calls.
- Blaszczyk explains that because Android keeps trying to process the same malicious message, the crash can happen repeatedly, potentially trapping the phone in a bootloop.
- Google developed a fix for the issue on June 15, and included it in October’s Android security updates for versions 14 through 17.
- GrapheneOS, a privacy-focused Android distribution, shipped the fix in its own security preview releases and stated that the patch will be part of the upcoming November 2026 Android Security Bulletin.
- However, until the update reaches users, a single malformed message can kill the com.android.phone process, causing it to crash on every boot.
- The researcher also released a proof-of-concept 'SMS of Death' app on GitHub, which remotely and silently sends a crafted 8-byte WAP Push PDU over SMS to a target handset.
- The exploit code is now public, and recovery from the bug often requires connecting to the phone using Android Debug Bridge (ADB) or a factory reset.
What's still developing
- Imagine dialing 911, only for your phone to suddenly drop the call.
- That’s the frightening scenario behind SMS of Death, a newly disclosed Android vulnerability that lets attackers remotely disrupt phones without the victim lifting a finger.
- Affiliate links on Android Authority may earn us a commission.
- Try searching for other cybersecurity topics or keywords.
- GrapheneOS said on its issue tracker that the fix went out in Android’s security preview patches, which Google shares with device makers ahead of each monthly bulletin, in mid-July.
- Google has marked the report “Won’t Fix” and treats it as a non-security issue, according to the researcher’s disclosure site.
- Android then tries to create a byte array of that size.
- The researcher shows that the five bytes 88 80 80 80 00 turn into -2147483648 after this conversion.