
Home · Entertainment · Oct 1 archive
Malware Campaign Uses Real ChatGPT Page to Spread Malware
Confirmed
In Short: Security researchers have uncovered a new malware campaign that uses a real ChatGPT page to trick victims into installing malware.
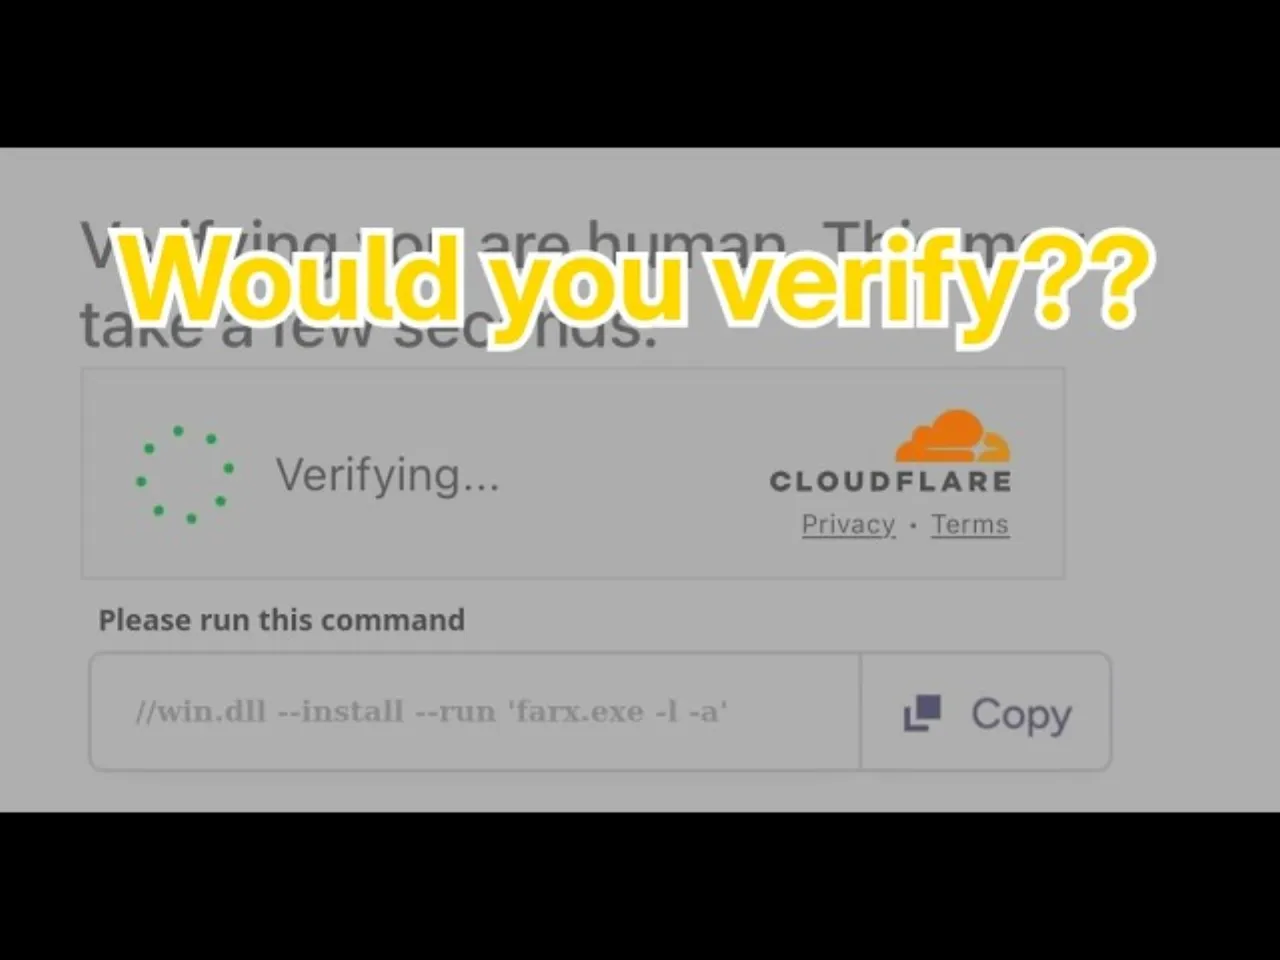
Security researchers have uncovered a new malware campaign that uses a real ChatGPT page to trick victims into installing malware.
Researchers at Huntress discovered that attackers are abusing ChatGPT’s Custom GPT feature to create a bot called “Plus 5.6,” designed to mimic an official OpenAI model.
Victims are directed to Plus 5.6 through sponsored Google search results, leading them to a fake GPT page that claims ChatGPT is experiencing availability issues and offers a 'backup domain.
This backup domain opens a Google Sites page that appears to be a Cloudflare security check, instructing users to copy and paste a command into Windows.
The malware campaign, which has been active since September, uses social engineering to trick victims into running attacker-supplied commands on their own machines.
The malware can give attackers extensive control over the infected PC, including the ability to view the screen, search files, use the webcam and microphone, capture system audio, and install more malware.
Researchers have also identified a new CustomGPT linked to the same campaign, and Huntress has warned ChatGPT users to be cautious.
The attackers developed a CustomGPT called Plus 5.6, which is designed to look like the real ChatGPT and impersonate legitimate product offerings.
The malware campaign uses a legitimate function of ChatGPT combined with ClickFix attacks to infect victims with malware.
ClickFix attacks are a popular technique among cybercriminals that use social engineering to trick victims into running attacker-supplied commands on their own machine.
The malware campaign has compromised thousands of legitimate small-business websites to spread this malware trap.
Researchers found that clinics, plumbing companies, online stores, and other businesses were among the victims.
What this adds
This report adds details on how the malware campaign uses social engineering and legitimate-looking websites to trick victims.
Researchers have identified a new CustomGPT linked to the same campaign, indicating ongoing efforts to spread the malware.
The malware campaign has compromised thousands of legitimate small-business websites, expanding the reach of the attack.
The attackers are using a combination of social engineering and legitimate-looking websites to trick victims into installing malware.
Background
Security researchers have uncovered a new malware campaign that uses a real ChatGPT page to trick victims into installing malware.
What's confirmed
- Security researchers have uncovered a new malware campaign that uses a real ChatGPT page to trick victims into installing malware.
- Researchers at Huntress discovered that attackers are abusing ChatGPT’s Custom GPT feature to create a bot called “Plus 5.6,” designed to mimic an official OpenAI model.
- Victims are directed to Plus 5.6 through sponsored Google search results, leading them to a fake GPT page that claims ChatGPT is experiencing availability issues and offers a 'backup domain.
- This backup domain opens a Google Sites page that appears to be a Cloudflare security check, instructing users to copy and paste a command into Windows.
- The malware campaign, which has been active since September, uses social engineering to trick victims into running attacker-supplied commands on their own machines.
- The malware can give attackers extensive control over the infected PC, including the ability to view the screen, search files, use the webcam and microphone, capture system audio, and install more malware.
- Researchers have also identified a new CustomGPT linked to the same campaign, and Huntress has warned ChatGPT users to be cautious.
- The attackers developed a CustomGPT called Plus 5.6, which is designed to look like the real ChatGPT and impersonate legitimate product offerings.
- The malware campaign uses a legitimate function of ChatGPT combined with ClickFix attacks to infect victims with malware.
- ClickFix attacks are a popular technique among cybercriminals that use social engineering to trick victims into running attacker-supplied commands on their own machine.
- The malware campaign has compromised thousands of legitimate small-business websites to spread this malware trap.
- Researchers found that clinics, plumbing companies, online stores, and other businesses were among the victims.
What's still developing
- Researchers have also spotted Android malware using Gemini to change its behavior while running.
- Instead of exploiting a software bug, ClickFix tricks you into doing the dangerous part yourself by presenting a fake problem and then offering a supposed fix.
- “Every step of the attack also borrows a brand people already trust, from ChatGPT and Google to Cloudflare and even Canon software. The takeaway is simple. No legitimate website will ever ask you to copy and paste a command to prove you’re human,” the company said.
- This link directs the user to a malicious Microsoft Software Installer (MSI) which is used to deploy a legitimate Canon-signed application the attackers have used to sideload malicious code, this ultimately establishes persistence on the machine and delivers remote access trojan (RAT) malware.
- CustomGPTs are personalized versions of ChatGPT which users can build to follow specific instructions and workflows.
- The superstar — and her Scottish fold cat named Olivia Benson — appeared alongside Mariska Hargitay, who plays Olivia Benson on Law & Order: Special Victims Unit, in a pre-recorded sketch that riffed on Hargitay’s hosting duties.
- Authorities also confirmed that at least two of the victims were nationals of Lesotho.
- Cofense’s Phishing Defense Center identified a phishing campaign spoofing ChatGPT and OpenAI billing alerts on September 18, 2026.
- With AI growing in popularity over the past few years, it is no surprise that threat actors are beginning to spoof ChatGPT, said Josh Varden of the Cofense Phishing Defense Center.
- Clicking the payment button first routes victims through a Google API redirect wrapper.
- It then drops them on a lookalike sign-in page copying OpenAI’s real logos and layout.
- Those attacks impersonate AI brands including ChatGPT, Microsoft Copilot, DeepSeek, and Anthropic’s Claude.